
News & Insights
Cloud Governance for Multi-Cloud and Hybrid Environments

Managed cloud services in Malaysia rarely start as a mess. They start as one team’s AWS account, then a second team’s Azure subscription, then a private cloud added for data residency, and within two years nobody can say with confidence who owns what or whether the same security policy applies everywhere. We work with Malaysian businesses on enterprise cloud and managed cloud services to bring that sprawl back under control, and this guide sets out the governance framework that keeps a multi-cloud or hybrid environment consistent as it grows.
This is not about picking fewer clouds. It is about applying the same standards, however many platforms you run, so growth adds capability instead of risk.
Why Multi-Cloud Environments Drift Into Sprawl
Sprawl is rarely a single bad decision. It is the accumulated result of good ones, made independently. A project team provisions a cloud account to move fast. A second team does the same for a different reason. A private cloud gets added for data residency, and nobody goes back to reconcile the three.
Left alone, this produces three specific problems: no single view of what exists across environments, security and access policy that quietly diverges between platforms, and cost and risk that grow faster than anyone budgeted for because nobody was tracking the total. None of this shows up as a single incident. It shows up as a slow loss of control that only becomes visible when something goes wrong.
Five Elements of a Cloud Governance Framework That Scales
A governance framework that works does not try to slow provisioning down. It defines the standards once and applies them automatically, so teams can move fast inside boundaries that are already set.
- Consistent identity and access. One identity system, federated into every cloud and on-premises environment in use, so access is granted and revoked from a single place rather than platform by platform.
- Clear ownership and accountability. Every account, subscription and environment has a named owner, kept in a central register, not tribal knowledge held by whoever set it up.
- Security and policy applied the same way across every platform. One baseline standard, with any platform-specific exception treated as something that needs a documented reason, not a default.
- Visibility across public and private clouds. A single inventory of what exists, where, and who is using it, so a question about your cloud footprint has one answer, not three different ones depending on who you ask.
- Guardrails that scale with growth. Preventive controls, policy enforced automatically at the point of provisioning, rather than periodic audits that only catch problems after they have already been running for months.
Where to Start: Sequencing a Governance Rollout
Trying to implement all five elements at once slows a governance programme down before it produces anything the business can see. Sequence it instead.
- Build the inventory first. You cannot govern what you cannot see, so a complete, accurate register of every account, subscription and environment comes before any policy work.
- Assign ownership against that inventory. Once you know what exists, name who is accountable for each item, and treat anything without an owner as the first thing to fix.
- Federate identity and access before writing new policy. Centralising access control closes the largest exposure fastest, and it is a prerequisite for enforcing anything else consistently.
- Apply the security baseline, then automate it as a guardrail. Bring every environment up to the same documented standard first, then move enforcement into the provisioning process itself so it stops depending on manual review.
- Schedule the review cadence last, once there is something stable to review. A recurring access and policy review only holds value once the first four steps are in place; scheduling it earlier just produces a report nobody can act on.
Governance Without Slowing Teams Down
The usual objection to governance is that it becomes a bottleneck: every new resource needs sign-off, and teams route around it to keep moving. Guardrails solve this differently from gates.
A gate stops a request and waits for a human to approve it. A guardrail is a standard built into the provisioning process itself, so a request that meets policy goes through automatically, and only genuine exceptions need a human. Pre-approved architecture patterns, automated policy checks and self-service within defined limits let teams provision quickly while staying inside the same standard every other team is held to. The goal is that following the standard is the fastest path, not the slowest one.
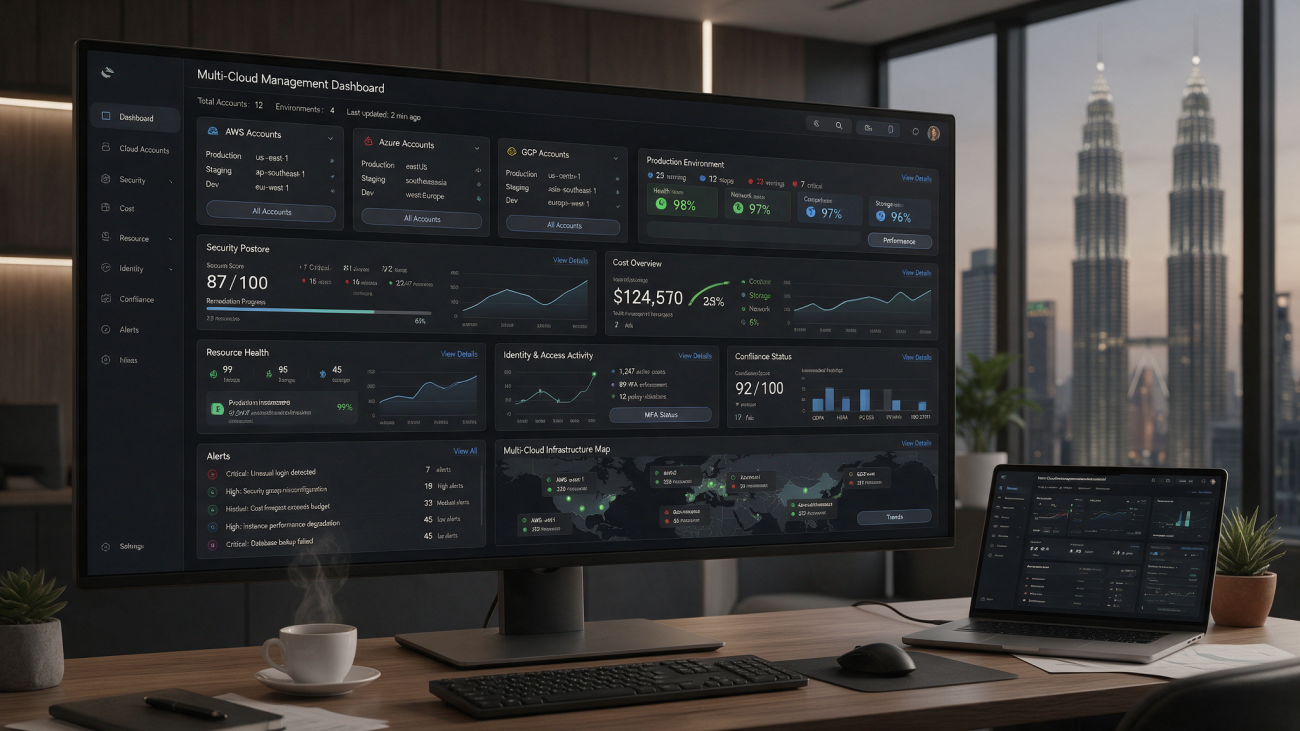
Governance for Managed Cloud Services in Malaysia: Where Compliance Fits
Personal Data Protection Act (PDPA), ISO/IEC 27001:2022 and BNM’s RMiT expectations all assume you can demonstrate that a control is actually running, consistently, across every environment holding the relevant data. For managed cloud services covering several platforms at once, that is a governance question before it is a technical one.
A documented control that only exists on paper, or that exists on one cloud account, but not the three others provisioned since, does not satisfy an auditor or a regulator. Governance is what turns a policy document into something you can actually prove: a named owner accountable for each environment, a single inventory to check against, and guardrails that keep the standard from drifting as new accounts get added. Without it, every audit becomes a fresh investigation into what is actually running where.
Common Governance Failures Worth Checking For
These recur across multi-cloud and hybrid environments regardless of provider, and each one is checkable without a full audit.
- Shadow accounts and subscriptions, provisioned outside the sanctioned process and invisible to the central inventory.
- Orphaned resources with no current owner, usually left behind when a project ends, or someone changes roles.
- Policy drift between environments, where a standard was applied when an account was created but never updated as the policy evolved.
- Guardrails that exist in a document but are not enforced, so provisioning still depends on someone remembering to check.
- Access reviews that happen once, at setup, and never again, leaving accumulated access nobody has re-validated.
Cloud Governance Checklist
Work through this before treating a multi-cloud or hybrid environment as governed. Each row needs a documented answer, not an assumption.
| Checklist item | What “done” looks like |
|---|---|
| Every cloud account and subscription inventoried | Central register, not spread across individual teams’ knowledge |
| Named owner assigned to every environment | Documented in the register, reviewed when staff change roles |
| Identity and access federated centrally | One system granting and revoking access across every platform |
| Security baseline applied consistently | Same standard on every cloud, exceptions documented with a reason |
| Guardrails enforced at provisioning, not just audited after | Policy checked automatically before a resource goes live |
| Access reviewed on a defined cadence | Not only at initial setup |
| Compliance obligations mapped to specific controls | PDPA, ISO 27001 and BNM RMiT each linked to what proves them |
Where We Fit
We are Strateq, and our cloud and cybersecurity practice is certified to ISO/IEC 27001:2022, so the governance standards in this guide are the ones our own operations are held to.
We are one of the few Malaysian providers that run their own data centres and work across public clouds including AWS, where we hold AWS Advanced Tier Partner status, and Azure, so we can help govern a multi-cloud or hybrid environment consistently rather than push you toward the one platform we prefer. Our Enterprise Business Solutions practice covers public, multi-, private and sovereign cloud as named capabilities under its cloud and cybersecurity work.
Use the checklist above as a starting audit of your own environment, and talk to our enterprise cloud team if the gaps need a second opinion.